Bottom Line
NIST’s new guidelines aim to secure online identity and access tokens from misuse, addressing risks like token forgery and unauthorized access. The publication provides implementation considerations for both federal agencies and cloud service providers, emphasizing cryptographic key protection and the need for secure token management in an increasingly digital world.
What Are Access Tokens and Why Do They Matter?
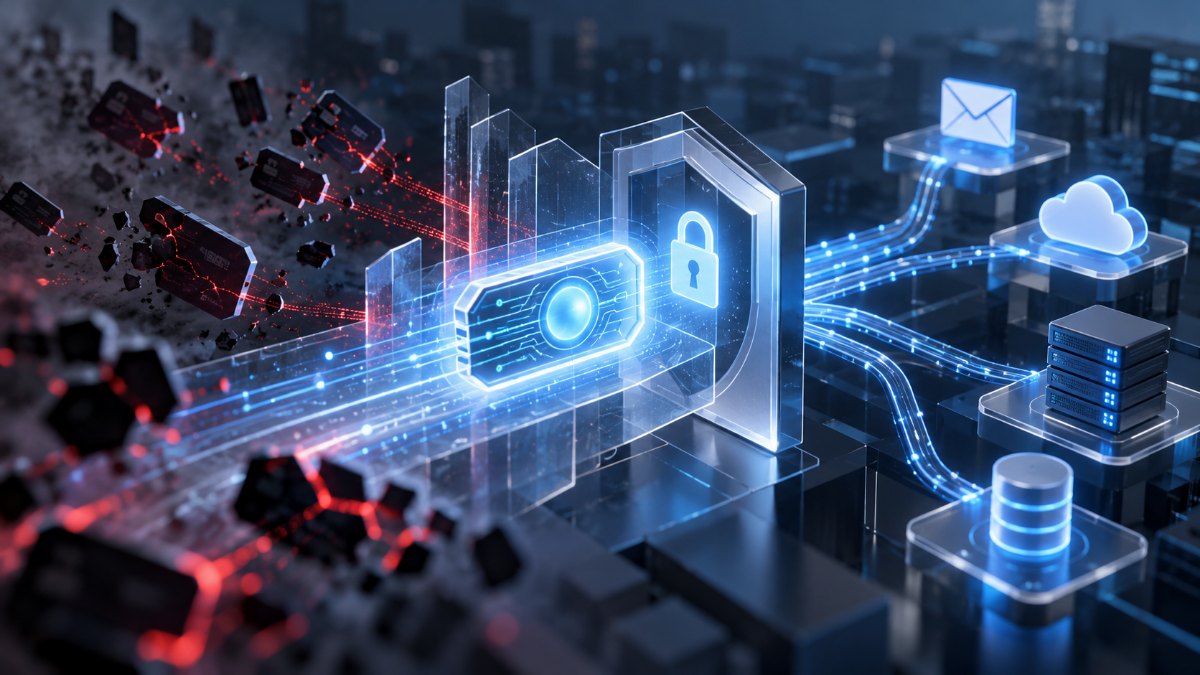
When you sign in to an online service like webmail, behind the scenes is often a token — a snippet of information identifying you and what online resources you are permitted to use, such as your inbox, contacts or other potentially sensitive information. They are also a key part of the access management infrastructure at most major cloud service providers (CSPs).
NIST’s New Guidelines for Token Security
Keeping these tokens safe is critical for protecting against unauthorized access, and it’s the goal of a newly finalized publication from the National Institute of Standards and Technology (NIST) and the Cybersecurity and Infrastructure Security Agency (CISA). The publication, titled Protecting Tokens and Assertions from Forgery, Theft, and Misuse (NIST IR 8587), provides implementation guidelines to help maintain the security of tokens, which are widely used in digital systems.
How the Guidelines Address Token Risks
The publication responds to NIST’s tasking in Executive Order 14306 and builds on recent updates to Special Publication 800-53, NIST’s catalog of security and privacy tools. It outlines a set of principles for both federal agencies and CSPs, delineating what provider and consumer organizations should do to ensure that data remains protected. One example cited in the report is an attack where foreign actors accessed agency email systems using forged tokens derived from a single stolen commercial signing key, resulting in over 60,000 emails being stolen from a single agency.
Key Changes and New Considerations
Among the most notable changes are guidelines regarding cryptographic key protection, which are now less prescriptive and more outcome-based, focusing on organizations’ overall capabilities. More advice is also included on cryptographic key usage, protection, and storage. New high-level considerations for handling AI and migration to post-quantum cryptography (PQC) standards are now included, though the publication does not offer a comprehensive set of tools for either topic.
Who Benefits From These Guidelines?
The report’s intended audience is both federal agencies, which need to understand how to configure services from their CSPs appropriately, and the CSPs themselves, which need to deliver secure products to these agencies. Galluzzo, one of the publication’s authors, said the authors revised the initial draft in response to reader feedback, ensuring that the final version reflects practical implementation considerations.
Verified Source Evidence
Verified source excerpt from National Institute of Standards and Technology:
When you sign in to an online service like webmail, behind the scenes is often a token — a snippet of information identifying you and what online resources you are permitted to use, such as your inbox, contacts or other potentially sensitive information. Keeping these tokens safe is critical for protecting against unauthorized access, and it’s the goal of a newly finalized publication from the National Institute of Standards and Technology (NIST) and the Cybersecurity and Infrastructure Security Agency (CISA).
Source: National Institute of Standards and Technology — NIST Finalizes Guidelines on Protecting Online Identity and Access Tokens From Misuse – National Institute of Standards and Technology (.gov).
—
Source Note
Source note: Source material: National Institute of Standards and Technology; document: NIST Finalizes Guidelines on Protecting Online Identity and Access Tokens From Misuse – National Institute of Standards and Technology (.gov).
Source Licensing
- Source policy: NIST Copyrights and Disclaimers (https://www.nist.gov/copyrights-disclaimers). Source: National Institute of Standards and Technology (NIST). NIST endorsement or recommendation is not implied.
Sources
1 independent organization · 1 source document. Links open the original material.
- 1National Institute of Standards and Technology NIST Finalizes Guidelines on Protecting Online Identity and Access Tokens From Misuse - National Institute of Standards and Technology (.gov)